AI governance operated from the inside
We are your AI Operating Partner. We don't recommend: we operate, build and deliver — with measurable impact on NPS, P&L and the AI adoption curve.
Request your pre-assessmentHave you inventoried every AI system that is already making decisions in your organisation?
The EU Artificial Intelligence Regulation (AI Act) entered into force in August 2024. Regulation (EU) 2026/1744 postponed the obligations for high-risk systems to December 2027 and August 2028, but the prohibitions, AI literacy, the rules for general-purpose models and transparency already apply. The deadline has moved; the obligations have not.
Source: Regulation (EU) 2026/1744 on EUR-Lex
Read the guide: AI Act for companiesAI Act — December 2027
An obligation to inventory, classify and govern high-risk AI systems. The prohibitions and AI literacy already apply.
DORA
Digital operational resilience for financial entities and their providers.
Spanish AI Governance Law
Oversight of and accountability for AI systems in production.
You have AI systems in production making decisions — in risk, credit, HR, customer service — with no inventory, no defined owner and no risk framework.
Most organisations don't have a vision problem. They have a systematic execution problem.
And the regulatory clock is ticking: traditional consulting delivers a PowerPoint nobody implements, not an operating model that works.
We don't recommend. We operate, build and deliver.
We are not judge and party
We assess without replacing and select the best vendors for your KPIs. We have no technology legacy to defend.
We co-operate, we don't advise
We operate inside your organisation. Impact is measured in NPS, conversion and P&L — not in PowerPoint deliverables nobody implements.
The knowledge stays
We design transferable operating models with an executor-agnostic methodology. We install capability, not dependency.
We govern with you, from the inside
We inventory your AI systems, define the risk framework and operate governance with your team, aligned with the AI Act.
Vendor-agnostic: we choose and operate the platform that best serves your KPIs.
If you already have AI running in production, this is for you.
You are a mid-sized company
You already have AI running in the business, but nobody is formally accountable for it and there are no clear rules. You decide fast and want to put it in order before it becomes a problem.
You lead it: CEO or General Management
You are a large regulated corporation
Banking, insurance, health, telco or FMCG: you have dozens of AI systems spread across the organisation, with no single inventory or common risk framework to govern them.
It concerns you: CRO, CDO or CAIO, with Legal
You operate with the AI Act deadline looming
AI-driven recruitment, credit scoring in fintech, health or pharma: your use cases fall into the high-risk categories and December 2027 sets the clock.
It falls to you: Compliance or DPO, with HR and Legal
You are a Latin American multinational operating in Europe
The AI Act reaches you through your European operations even if your headquarters are elsewhere. You need coordinated regional governance, not piecemeal country-by-country fixes.
You coordinate it: CLO or CCO, with the Data team
Real results in some of the largest companies in Ibero-America.
+40%
productivity in the first year operating with Scotiabank.
15 years
as Coca-Cola's operating partner in its digital ecosystems.
25+ years
proving that product and service, with technology, can scale.
Track record operating inside
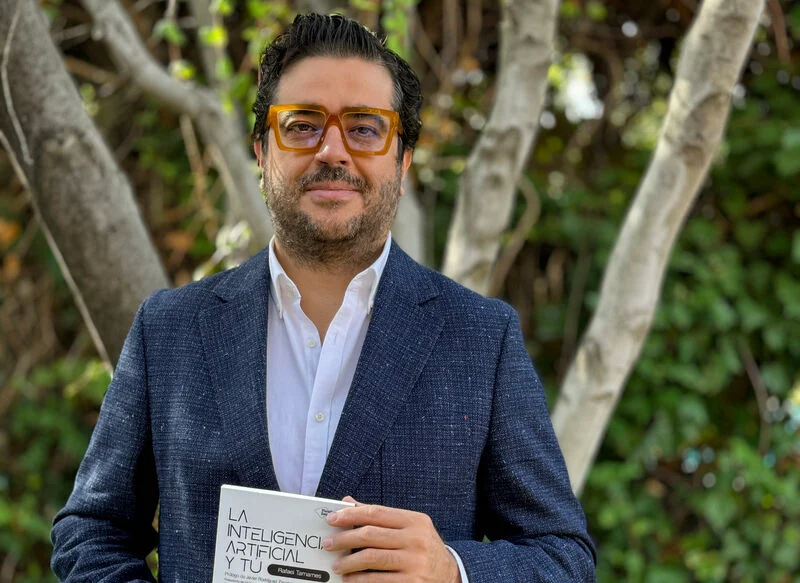
Led by Rafael Tamames, founder of Vivid Vision, tech entrepreneur and LinkedIn Top Voice in AI and Entrepreneurship. Founder of Findasense — one of the 50 largest startup exits in Spain's history, an IESE case study and a B Corp company. More than 25 years building, scaling and operating businesses with technology.
“I have worked with Rafael in several professional capacities, as a client, as a speaker and as an adviser. Rafael has a natural talent for spotting digital and technology trends. He is able, like no one else, to identify consumer insights and find the right technologies to improve people's lives. He is a great student of different leadership models and a benchmark for business and professional values and ethics.”
 Carlos Oliveira (Spain)Executive Customer Lab Director at EVO Banco
We inspire, train and operate with AI.
Inspire
We spark the high-level strategic conversation: keynotes and strategy sessions that move the C-Level to action.
Activate
We train leadership layers in AI and activate the organisation's AI Champions.
Operate
We assess and execute inside the organisation: AI Governance and new businesses.
From pre-assessment to governance in operation, in a clear process.
Pre-assessment
We map your AI systems in production, their risks and your priorities under the AI Act and DORA. In weeks, not months.
Inventory and risk framework
We build the single inventory and the governance model: risk classification, owners, controls and traceability.
Operation with your team
We deploy governance operating inside your organisation, prioritising the highest-risk systems. Measurable impact on NPS, P&L and adoption.
Handover
The operating model and the knowledge stay with you. We install capability, not dependency.
Frequently asked questions about AI governance.
What is AI governance?
It is the set of processes, controls and responsibilities that allow an organisation to inventory, classify, oversee and be accountable for the AI systems that are already making decisions in production. It covers risks, bias, traceability, regulatory compliance and human oversight, so that AI operates safely, auditably and in line with the business.
What does the EU AI Act require and when does it apply?
The AI Act classifies AI systems by risk level and requires an inventory, risk management, documentation, human oversight and transparency. It entered into force in August 2024 with phased application: prohibited practices and AI literacy from February 2025, general-purpose models from August 2025 and transparency from August 2026. Regulation (EU) 2026/1744 postponed the obligations for high-risk systems to 2 December 2027 (Annex III) and 2 August 2028 (Annex I). The deadline has moved, not the obligations: that is why preparation must start now.
Who does DORA apply to and what does it require?
DORA (Digital Operational Resilience Act) applies to EU financial entities —banks, insurers, asset managers— and their critical technology providers, and has been fully applicable since 17 January 2025. It requires digital operational resilience: ICT risk management, testing, incident reporting and third-party control, which includes the AI systems that support critical processes.
What is ISO 42001 and does my company need it?
ISO/IEC 42001 is the first certifiable international standard for an artificial intelligence management system (AIMS): it defines how to govern, oversee and continually improve an organisation's AI systems. Any company that runs AI in production and wants to demonstrate responsible governance to customers, investors or regulators needs it, and it complements the AI Act: the standard provides the management framework that makes regulatory compliance easier.
Do I need a Chief AI Officer (CAIO) in my company?
A Chief AI Officer (CAIO) is the person who takes executive responsibility for AI strategy, risk and governance in the organisation. If you already have AI systems making decisions in production, you need that responsibility assigned —whether a dedicated CAIO or an equivalent role— because the AI Act requires human oversight and accountability. We help activate that role and its operating framework from the inside.
How is Vivid Vision different from a traditional consultancy?
We don't recommend: we operate. Instead of delivering a PowerPoint report, we co-operate inside your organisation and our impact is measured in NPS, P&L and the AI adoption curve. We are vendor-agnostic —with no technology of our own to defend— and the knowledge stays with you through transferable operating models.
How long does it take for an AI governance programme to be operational?
It depends on size and regulatory exposure, but we start with a pre-assessment that, in a few weeks, maps your AI systems in production, their risks and compliance priorities. From there we deploy the governance model incrementally, prioritising the highest-risk systems with a view to the AI Act and DORA.
What does the pre-assessment include?
A working session in which we review your AI systems in production, identify gaps against the AI Act, DORA and Spanish regulation, and give you a risk map with actionable priorities. No commitment and no cost: it is the starting point to decide whether it makes sense to operate together.
Understand the regulatory framework before you act.
AI Act for companies: requirements and deadlines
Risk levels, obligations, updated deadlines up to 2028 and fines of up to €35M. The guide to the EU AI Regulation for Spanish companies.
Read the guideISO 42001: the AI management standard
What an AI management system (AIMS) requires, how it is certified and how it differs from the AI Act —and why they complement each other.
Read the guideAI governance framework: roles and the CAIO
The building blocks of an AI governance framework —policy, inventory, committee, controls— and the roles that sustain it, including the CAIO.
Read the guideAESIA: Spain's AI agency
What AESIA is, Spain's national authority for the AI Act: how it was created, its headquarters in A Coruña, its powers and sanctioning authority.
Read the guideRequest your AI Governance pre-assessment
The AI Act has moved the deadline, not the obligations. In 16 weeks we inventory your AI systems, define the risk framework and leave governance operating with your team.
What happens after you write to us
A reply within 24–48 working hours
We read your message and email you to propose a time.
A first 30-minute call
We talk about your AI systems and what the pre-assessment would cover.
No commitment
After the call you decide whether to go further. If we are not a fit, we will tell you.

